
API of Allure TestOps
The API is for teams that need programmatic access to Allure TestOps data and administration rather than only UI workflows. The entry point is the Swagger UI served by your own Allure TestOps instance at <your Allure TestOps domain>/swagger-ui.html.
Test result upload
Use the public API for reading and managing Allure TestOps entities.
Do not build your own direct test-results upload client against internal upload endpoints. Upload workflows are supported only through Qameta-maintained tools such as CI plugins and
allurectl.
Use one of these supported upload paths instead:
- Integrations for CI plugins and connected build systems;
- allurectl for CLI-driven upload and selective execution.
Find operations in Swagger UI
In the upper-right corner, click the Select a definition drop-down list.
Choose the appropriate section:
- Report Service: API methods for creating, updating, and retrieving information about test cases, test results, launches, etc.
- UAA Service: API methods for managing user access permissions in Allure TestOps, adding new users, and working with Allure TestOps licenses.
- All Services: all available Allure TestOps API methods (a combination of the Report Service and UAA Service sections).

Discover API calls from the UI
Not every task has a dedicated documentation page. If you can already do something in the UI, perform the action once with browser DevTools open and reuse the request that the UI sends:
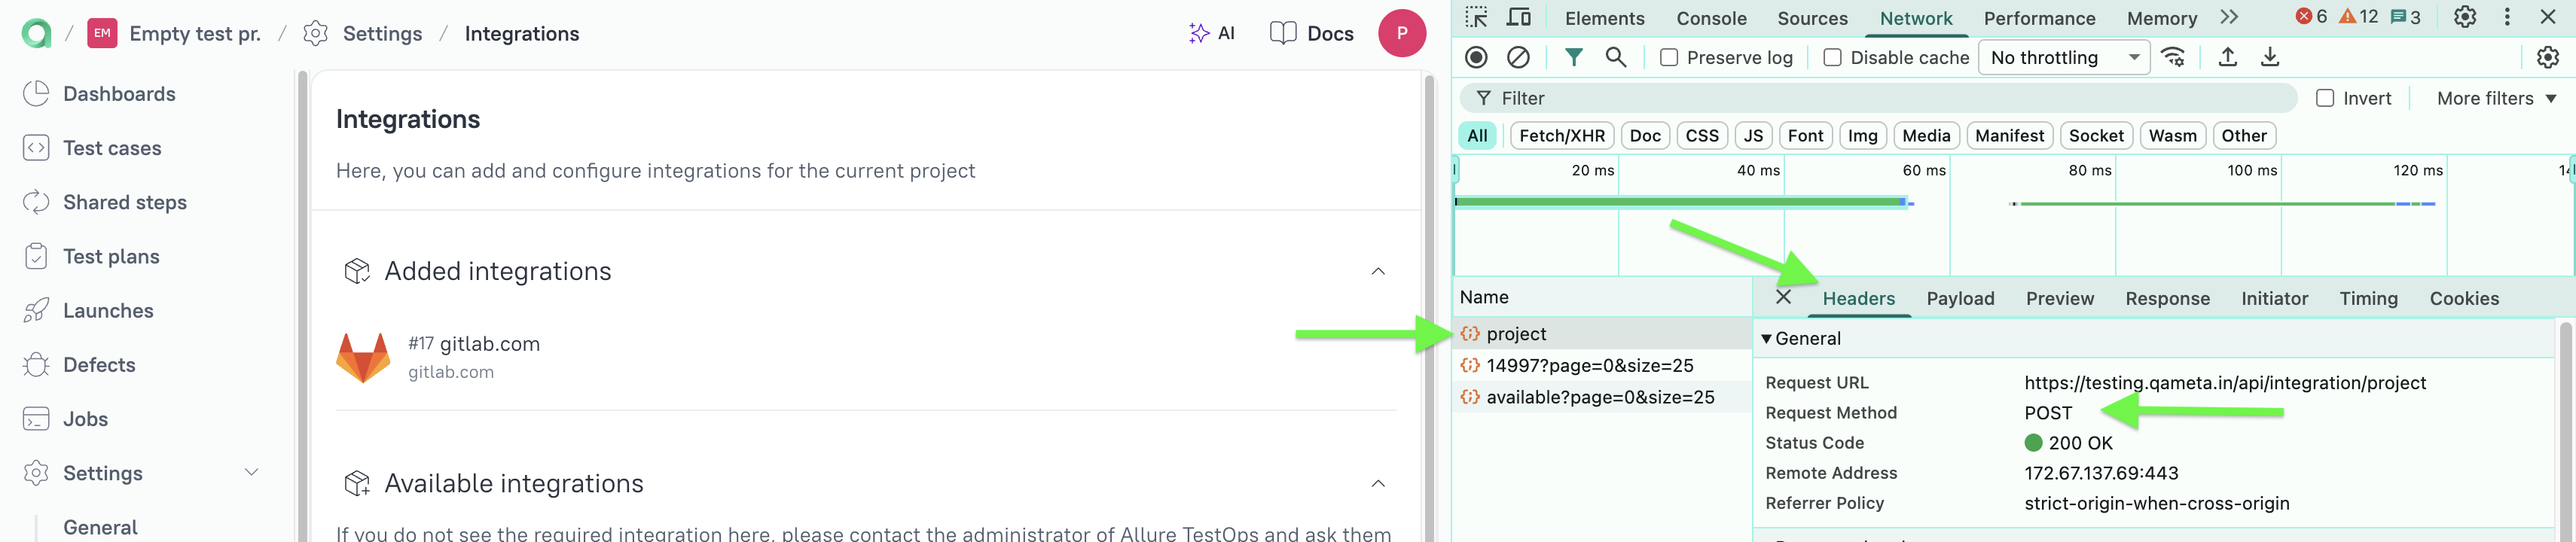
Open browser DevTools and switch to the Network tab. To hide requests for scripts, styles, and images, select the Fetch/XHR filter.
Perform the action in the UI, for example, click Add integration.
Select the request that appeared after the action.
On the Headers tab, note the Request URL and Request Method.
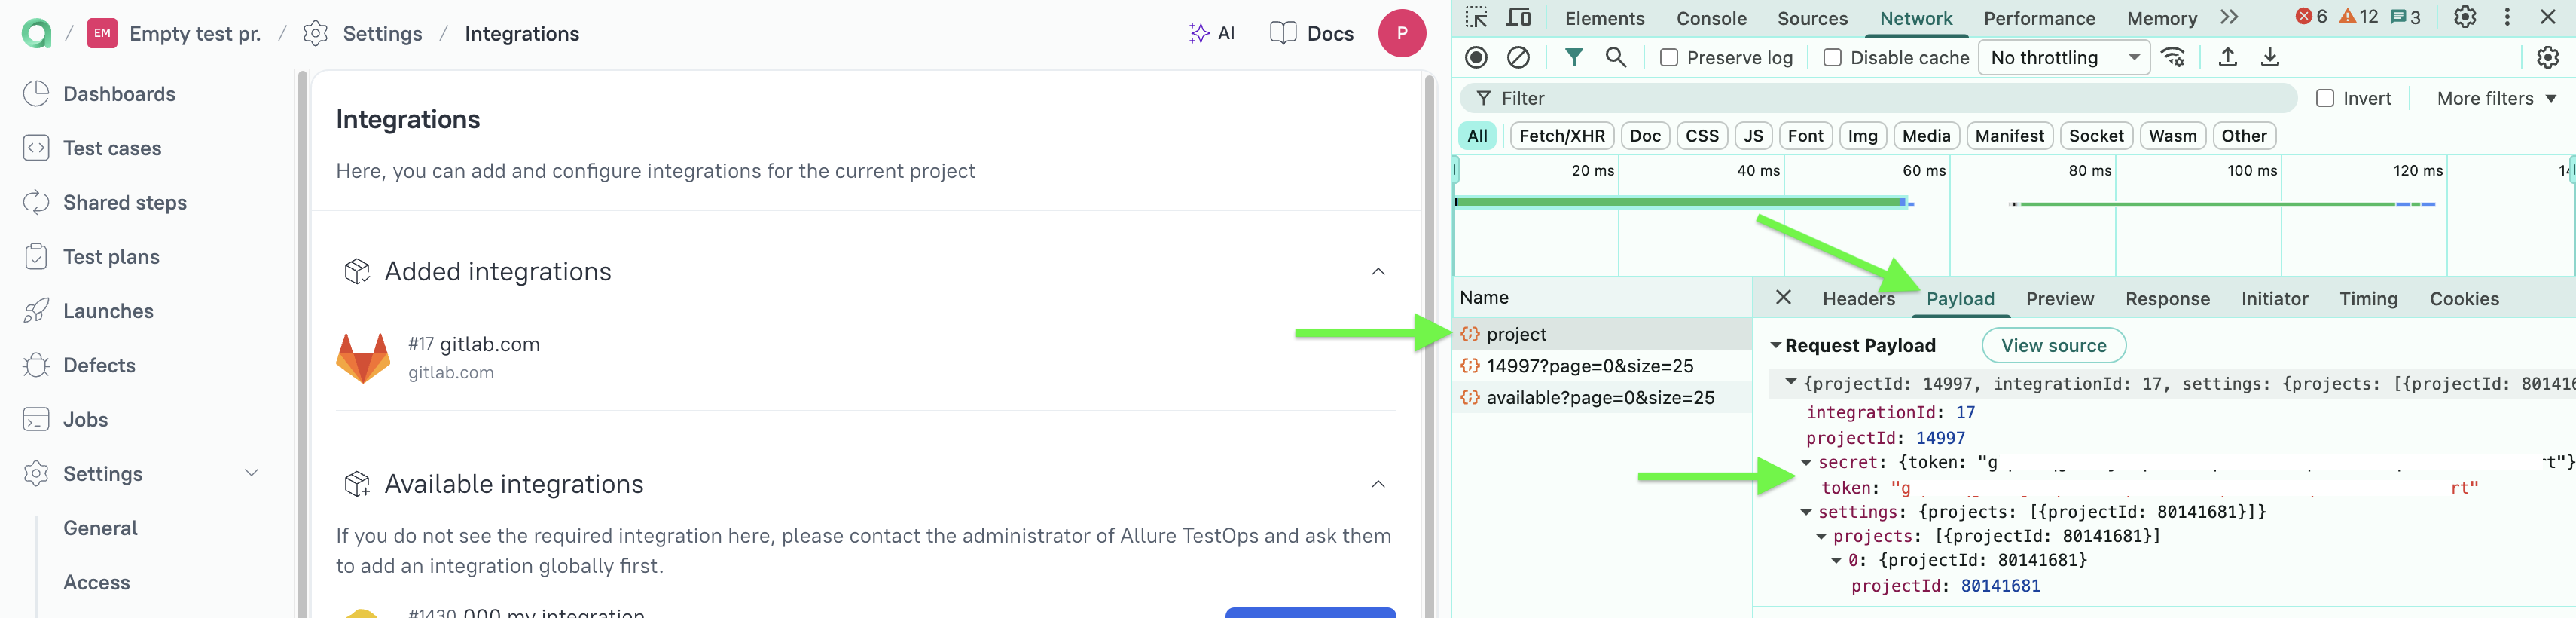
On the Payload tab, note the request body: field names, nesting, and value types.
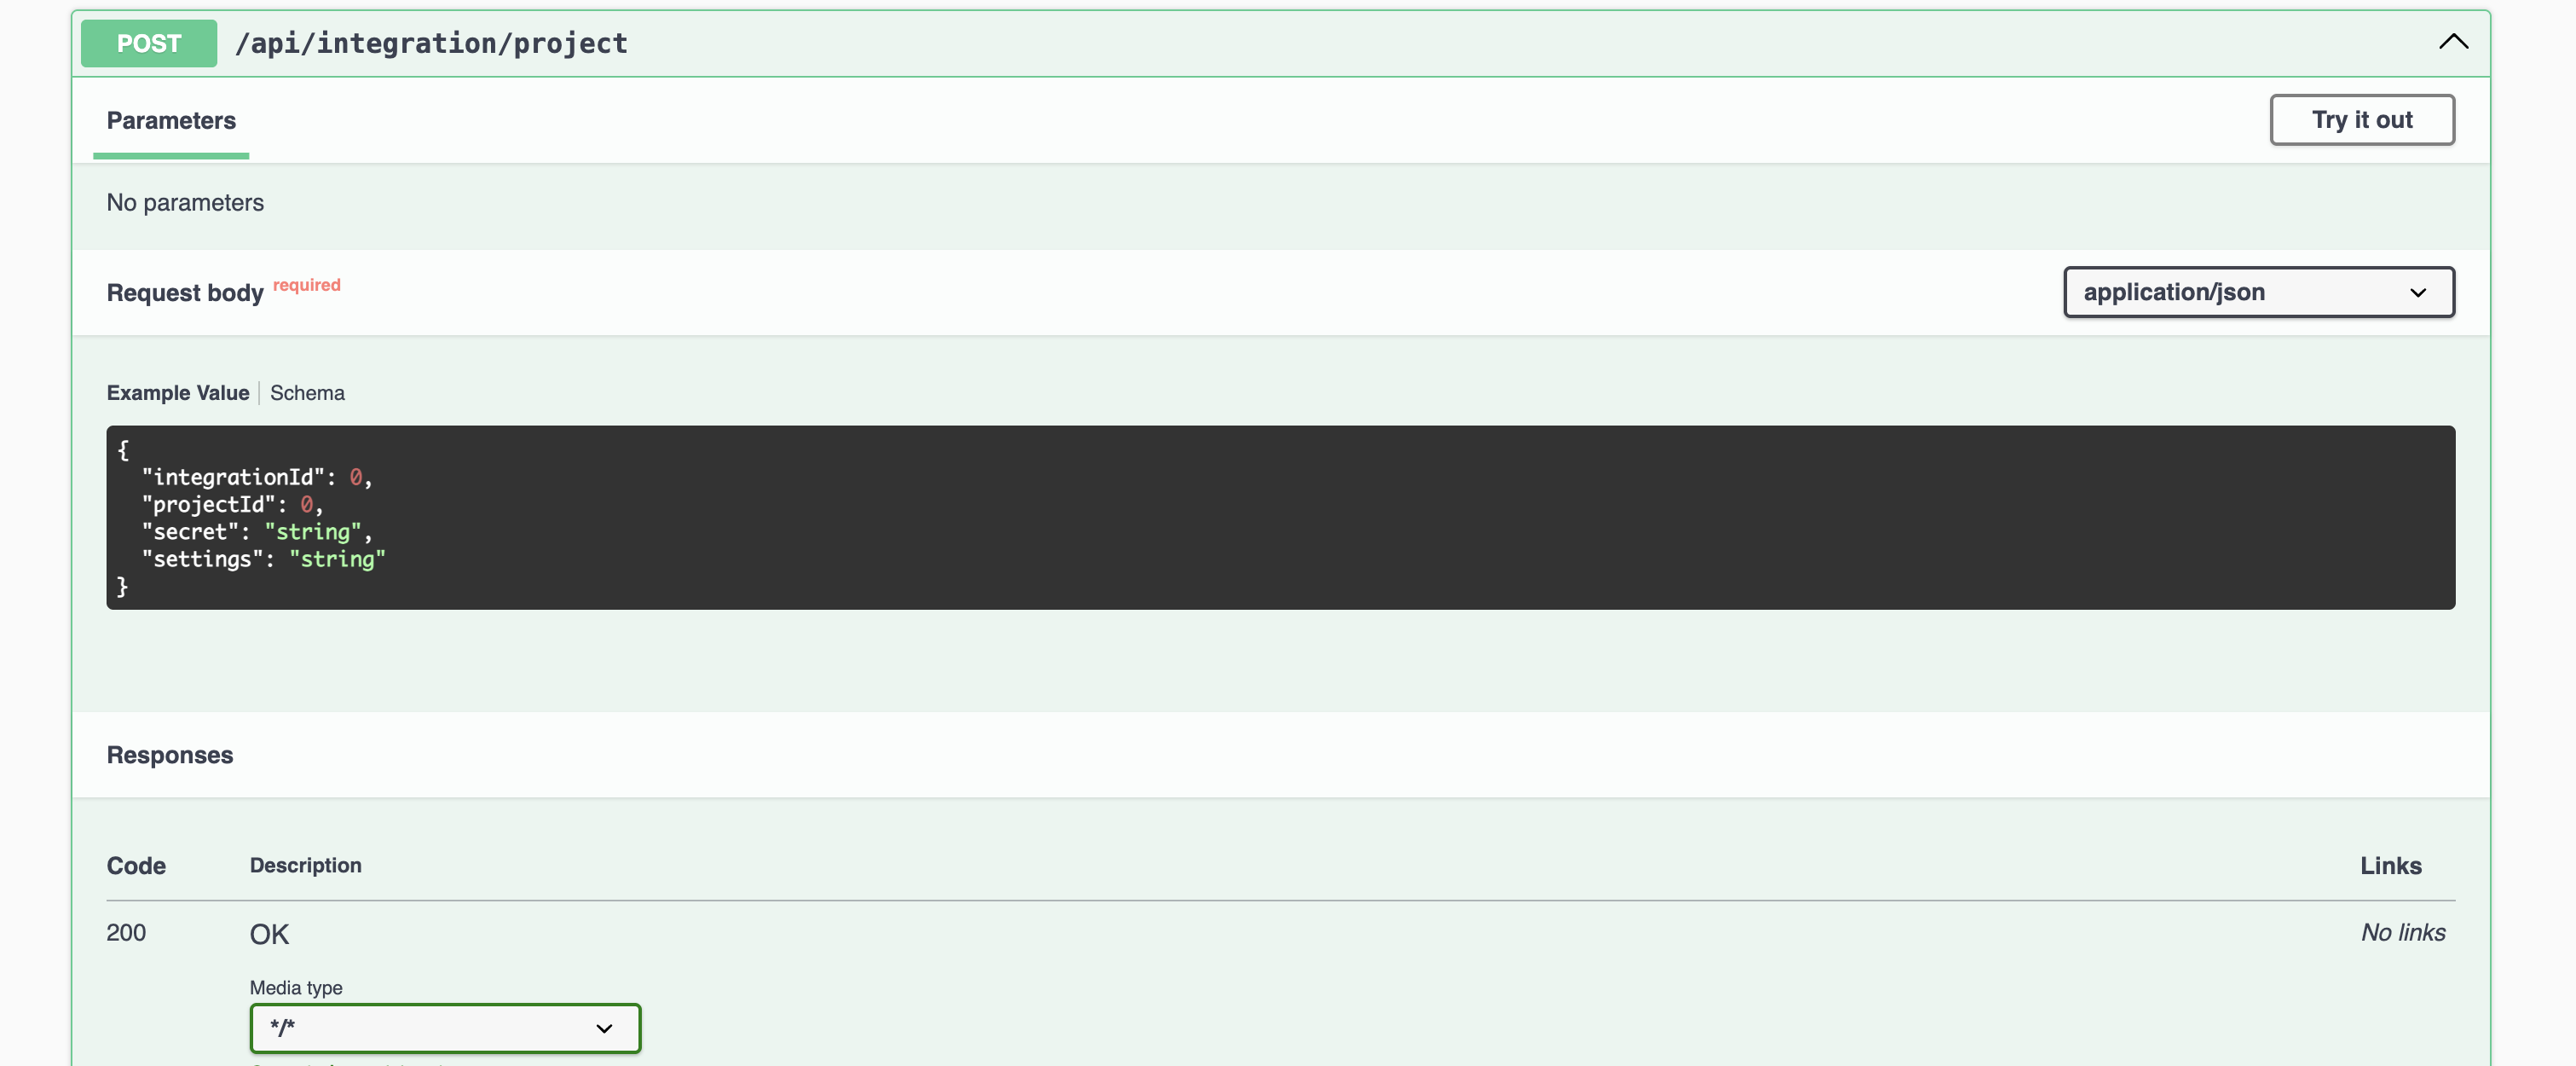
In Swagger UI, search the page for the request path to find the operation description, the required fields, and the response schema.
Reproduce the call outside the browser with a Bearer token, see Authentication.
Build scripts only on operations that are listed in Swagger UI. If a request you see in DevTools is missing from Swagger UI, do not rely on it in automation.
Example: add an integration to a project
An administrator adds an integration globally, and each project connects it with its own credentials, so different teams do not share access to each other's CI or issue tracker projects. To repeat this for many projects, perform it once in the UI:
- In a project, go to Settings → Integrations.
- In the Available integrations section, click Add integration next to the integration you need.
- Enter the credentials, check them with Test connection, and click Add integration.
The UI sends POST /api/integration/project. The same call for a GitLab integration looks like this:
curl -s -X POST "${ENDPOINT}/api/integration/project" \
     --header "Authorization: Bearer ${JWT_TOKEN}" \
     --header "Content-Type: application/json" \
     --data '{
       "integrationId": 17,
       "projectId": 14997,
       "secret": { "token": "<GitLab personal access token>" },
       "settings": { "projects": [ { "projectId": 80141681 } ] }
     }'
Where:
ENDPOINTandJWT_TOKENare the instance URL and the Bearer token from Authentication.integrationIdis the ID of the global integration. The UI shows it with#next to the integration name, for example,#17 gitlab.com.projectIdis the ID of the Allure TestOps project.secretandsettingshold the credentials and settings of the integration. Their fields depend on the integration type: in this example, GitLab expects a personal access token and the IDs of the GitLab projects. Copy the structure from the Payload tab of your own request.
Try operations directly in Swagger UI
Swagger UI lets you execute the request against your own instance and inspect the resulting curl example, parameters, and response payload.

Authentication
Swagger UI uses your current browser session automatically. External scripts and integrations should use a Bearer token derived from your personal API token.
Create the personal API token in User menu and API tokens before you automate API calls.
Generate a Bearer token
The example below exchanges a personal API token for a short-lived Bearer token:
export ENDPOINT="https://testops.example.com"
export USER_TOKEN="ef06773a-544b-4f0b-ad53-5a11972c8b74"

echo "Obtaining jwt token"
JWT_TOKEN=$(curl -s -X POST "${ENDPOINT}/api/uaa/oauth/token" \
     --header "Expect:" \
     --header "Accept: application/json" \
     --form "grant_type=apitoken" \
     --form "scope=openid" \
     --form "token=${USER_TOKEN}" \
     | jq -r .access_token)
Use the Bearer token in requests
echo "Getting user information"

curl -s -G "${ENDPOINT}/api/uaa/me" \
     --header "Accept: application/json" \
     --header "Authorization: Bearer ${JWT_TOKEN}"
Bearer token validity
The Bearer token is short-lived. The default validity is controlled by the ALLURE_JWT_ACCESS_TOKEN_VALIDITY_SECONDS parameter in your instance configuration. Re-generate the token when it expires.
Related pages
- User menu and API tokens for creating or revoking the personal token.
- AQL if your API work depends on reusable query expressions.
- Integrations if the real goal is supported CI or issue-tracker connectivity rather than direct API scripting.
